
Every alert cites its evidence. Credibility, confidence, what remains uncertain and every citation policy allows.
Customer alertsAdversary intelligence · Evidence-first
Know what an adversary knows about you.
Nullstar watches the underground for your organisation: access for sale, identities already exposed, data already published. It turns that into evidence-backed alerts and a reviewed view of how an adversary could come at you.
- Evidence-backed
- Analyst-reviewed
- No engagement with actors
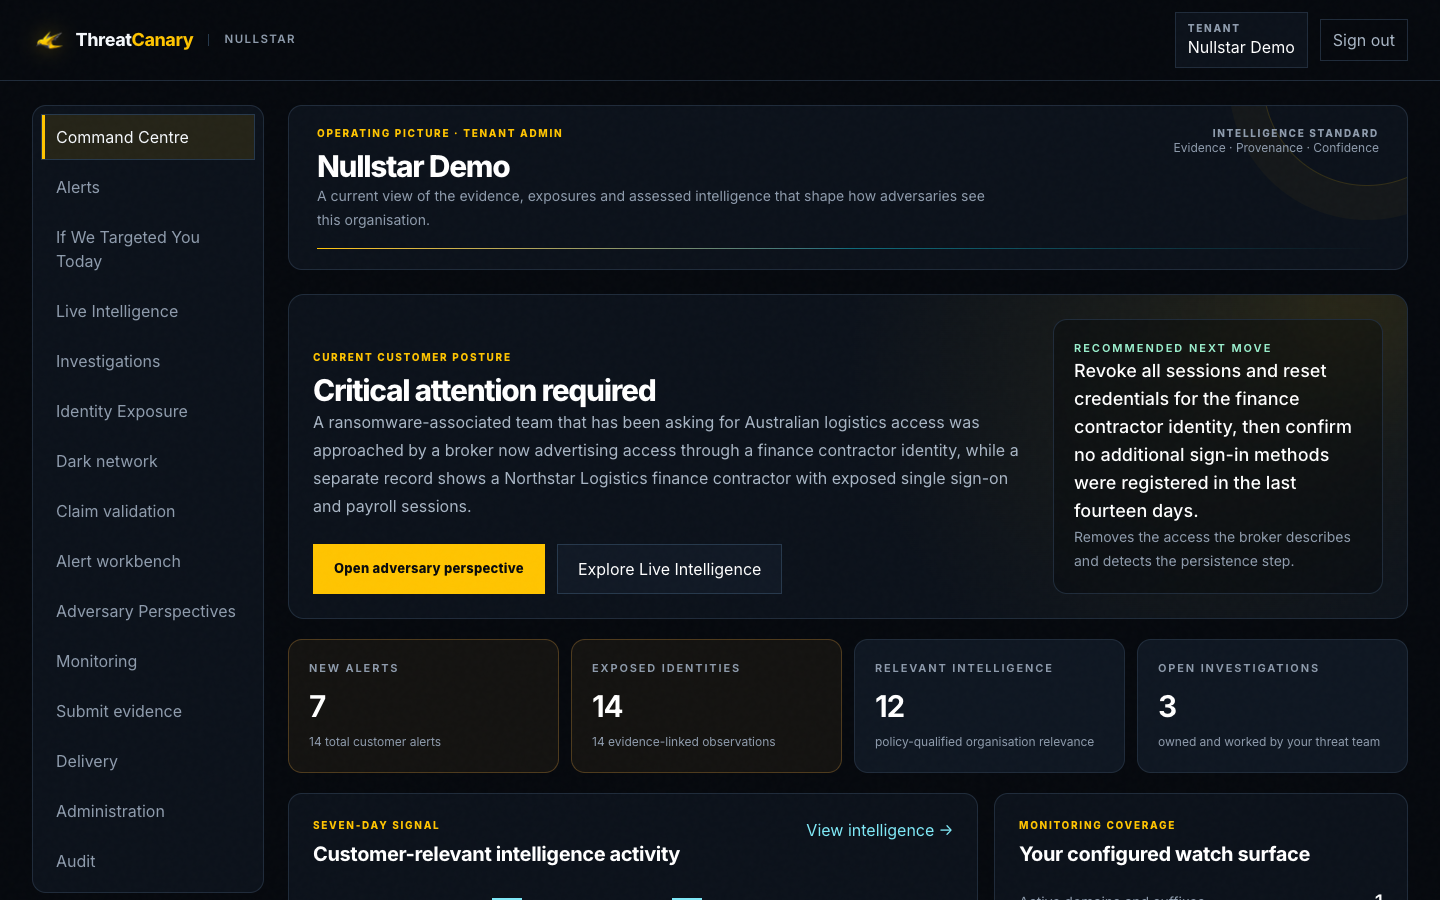
7New alerts
14Exposed identities
12Relevant intelligence
Current posture · example
Critical attention requiredA ransomware crew is shopping for access to Australian logistics firms, via your finance contractor. Revoke all sessions and reset that identity’s credentials.
Adversaries already have a view of you. Nullstar shows you theirs.
Not a feed, not a scanner. Preserved evidence, assessed by analysts, delivered as decisions your team can defend.
What you get
Three views of the same adversary.
Each one is built from the same preserved evidence and reviewed before you see it.
Adversary Perspective
If We Targeted You Today
A reviewed, evidence-backed hypothesis of the path an adversary could assemble against you now — with the validation your team can run.
ExploreLive Intelligence
What changed, assessed
Underground, malware and identity signals, continuously collected and assessed for the global ecosystem, your sector and your organisation.
ExploreIdentity Exposure
The identities that open doors
Compromised credentials and sessions connected to the portals and relationships that could make them operationally useful.
ExploreCollection finds the signal. Resolution explains it. Nullstar proves it with evidence — all of it on one tenant-isolated graph. How the platform is built.
Worked example
See how a listing becomes a decision.
One case, end to end: a broker’s listing, an exposed contractor identity, and the alert that reached the customer with a recommended move.
collectBroker listing captured: access to an Australian logistics firm, sold via a finance contractor identity.
preserveRaw listing, source metadata and capture time stored immutably. Provenance recorded.
resolveContractor identity matched to exposed single sign-on sessions in a separate stealer-log record.
assessAnalyst validates the claim, drafts the alert and the adversary hypothesis; a peer reviews both.
deliverCritical alert published with the recommended move: revoke sessions, reset the contractor’s credentials.
Hop 1 · Listing
Access for sale
A broker advertises a way into Australian logistics firms.
evidenceHop 2 · Identity
Finance contractor
The route runs through a named contractor identity.
evidenceHop 3 · Access
Exposed SSO sessions
The same identity appears in a stealer log with live sessions.
evidenceHop 4 · Impact
Critical attention required
Revoke all sessions and reset credentials for the contractor identity.
recommended move
The workspace
Every answer, one workspace.
Posture, assessments, live signal, dark-network coverage and identity exposure — every screen built on the same preserved evidence.
Intelligence command centreCurrent posture, the recommended next move, seven-day signal and the exposures that changed — on one screen.
Outcomes
What changes when the evidence is there.
Two analysts behind every call. Author, challenge, approve. Nothing reaches a customer unreviewed.
Peer reviewAdversary hypotheses you can test. Each perspective carries the validation steps your team can run today.
If We Targeted You TodayIdentities tied to the doors they open. Exposed credentials connected to portals and relationships, not a flat list.
Identity ExposureQuestions that keep their lineage. Investigations bind to the exact revision they came from.
InvestigationsYour tenant, your data, audited. Tenant-scoped storage, single sign-on and a tamper-evident audit history.
PlatformPipeline
From underground signal to a defensible decision.
Five stages, each with a rule it must keep. The doctrine behind them
01
Collect
Governed connectors gather underground listings, leak publications, malware infrastructure and identity material from forums, markets, leak sites, Telegram and stealer logs.
02
Preserve
Raw evidence is kept immutable, with its provenance. Uncertainty is recorded, not smoothed away. Model output is never treated as evidence.
03
Resolve
Each record is parsed and enriched, duplicates and reposts are detected, entities are resolved, and the graph can always be rebuilt from the records.
04
Assess
Analysts validate claims, author alerts and adversary perspectives, and peer-review before anything reaches a customer.
05
Deliver
Customers get relevance-scored alerts, the command centre, investigations, notifications, an API and webhooks.
- Evidence before narrative
- Models assist; they never act
- No deceptive participation
- Tenant isolation by construction
FAQ
Questions security teams ask first.
01Is Nullstar an attack-surface or vulnerability scanner?
No. Nullstar is adversary intelligence — what adversaries know, hold and discuss about you. Attack-surface discovery, vulnerability scanning and exploit validation are out of scope for Nullstar; that is what ThreatCanary’s Exposure Intelligence, API Security and AI Offensive Security products do. Together they cover both sides of the same question.
02Does the platform interact with criminal actors?
No. Nullstar never messages, negotiates, buys or tests credentials. Some sources hide content behind a fixed action; where one is taken it is scripted, limited, logged and approved in advance, and it can be switched off at once. Models never compose, select, initiate or trigger contact with criminal actors.
03What does a Nullstar alert contain?
A customer-safe assessment with credibility, confidence rationale, uncertainty and alternatives, potential impact, recommended defensive validation and the evidence citations policy allows. If a source is held back you are told how many, so an alert never implies false certainty.
04How does “If We Targeted You Today” work?
Analysts assemble an adversary hypothesis from preserved evidence and a peer reviews it. You see the current revision, its history and the validation steps you can run. It is a reviewed hypothesis, not a prediction of a specific attack.
05How is customer data protected?
Tenant-scoped storage, separate object storage for evidence, role-based access, single sign-on with MFA for privileged users, and a tamper-evident audit history. Customer-confidential context stays inside its tenant, and the workspace never renders images from collected content.
06What does a monitoring domain trigger?
Nothing outward. Monitoring domains and identifiers are matching keys only — adding one never triggers DNS lookups, discovery, scanning or contact with the organisation.
Ready to see your organisation the way an adversary does?
Request access, or explore the interactive demo first.
Customer workspace
Every module, on one tenant-isolated workspace.
Customer workspace
What your security team sees — posture, alerts, the adversary’s likely path and the identities that make it possible, each traceable to evidence.
Intelligence command centre
Posture, recommended next move, seven-day signal and the priority intelligence that changed for you — on one screen.
ExploreIf We Targeted You Today
A reviewed, evidence-backed hypothesis of the path an adversary could assemble against you now.
ExploreLive Intelligence
Assessed changes across the global ecosystem, your sector and your monitored organisation.
ExploreIdentity Exposure
Compromised identities connected to the portals and relationships that make them operationally useful.
ExploreDark-network intelligence
Underground monitoring coverage, community activity and the account histories behind the intelligence.
ExploreInvestigations
Turn delivered intelligence into a traceable question, response and decision history.
Explore