Capability architecture
See what changed, and why it matters to you.
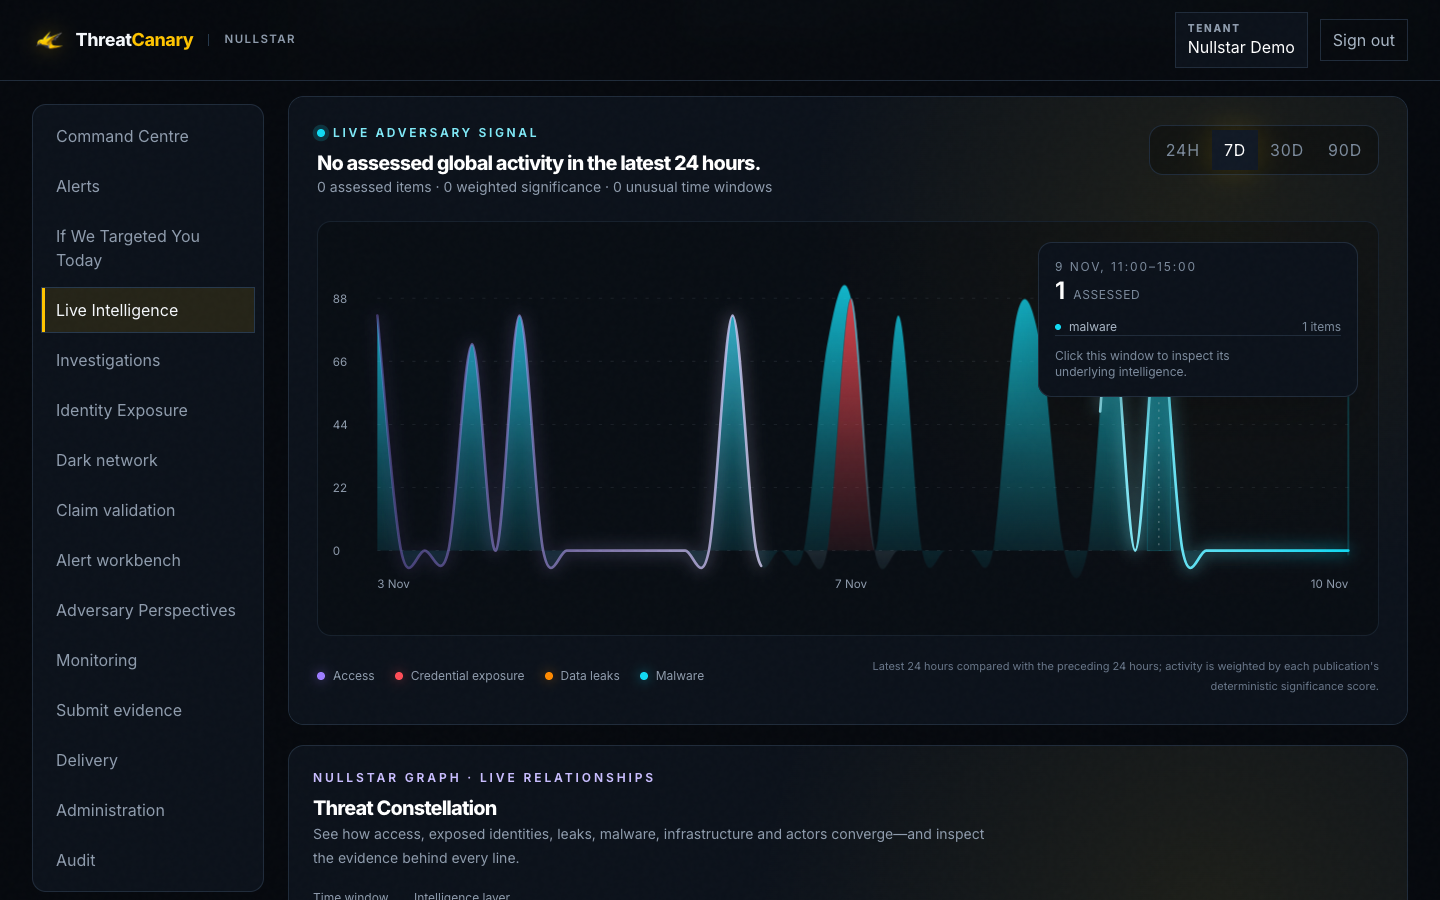
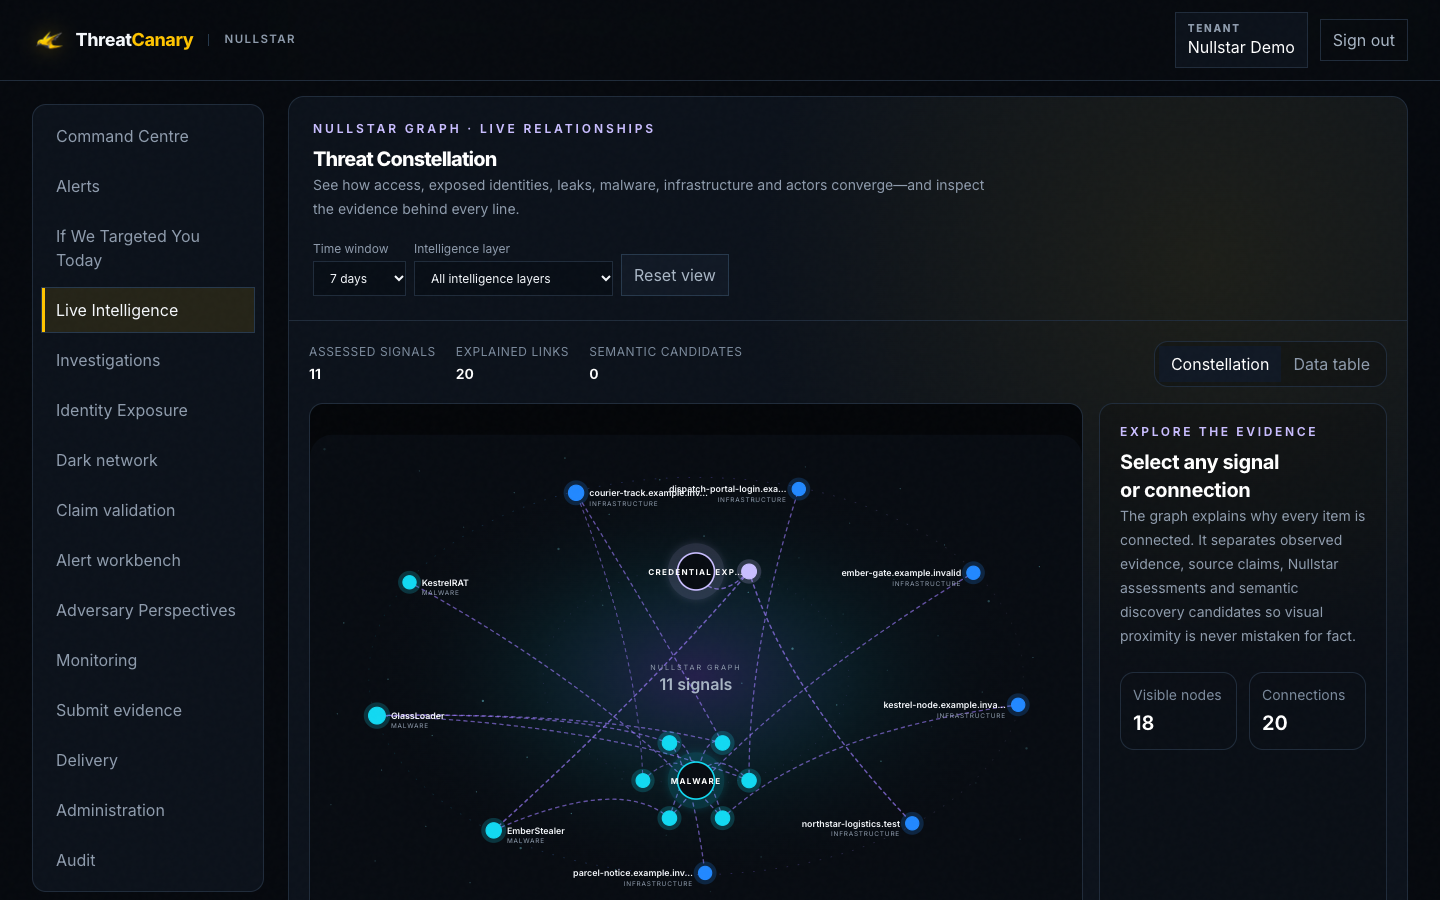
An activity timeline, a threat constellation and a pattern explorer sit over the same preserved evidence, so every spike and every relationship can be opened to its source.
01Why it matters
- Underground activity moves in bursts. A new access broker, a stealer-log dump or a leak publication can change your picture in a day.
- Raw feeds bury the change that matters to you under everything that happened to everyone.
- Relationships between access, identities, leaks, malware and actors are where the risk lives — not in any one record.
02ThreatCanary approach
- Governed connectors collect continuously from forums, markets, leak sites, Telegram and stealer logs; every record is preserved with provenance.
- Signal is assessed at three scopes — the global ecosystem, your sector and your organisation — and weighted by significance.
- Duplicates and reposts are detected and entities resolved, so the timeline reflects events rather than noise.
03What you see
- A seven-day adversary-signal timeline of access, credential exposure, data-leak and malware activity, with every window inspectable.
- A threat constellation showing how access, exposed identities, leaks, malware, infrastructure and actors connect, with the evidence behind every line.
- A pattern explorer for the recurring behaviours behind the signal.
04Evidence produced
- Assessed activity series with the preserved records behind each window.
- Resolved entities and relationships that can always be rebuilt from the records.
- The changed intelligence that feeds your command centre and alerts.