Capability architecture
A hypothesis you can test, not a prediction you have to trust.
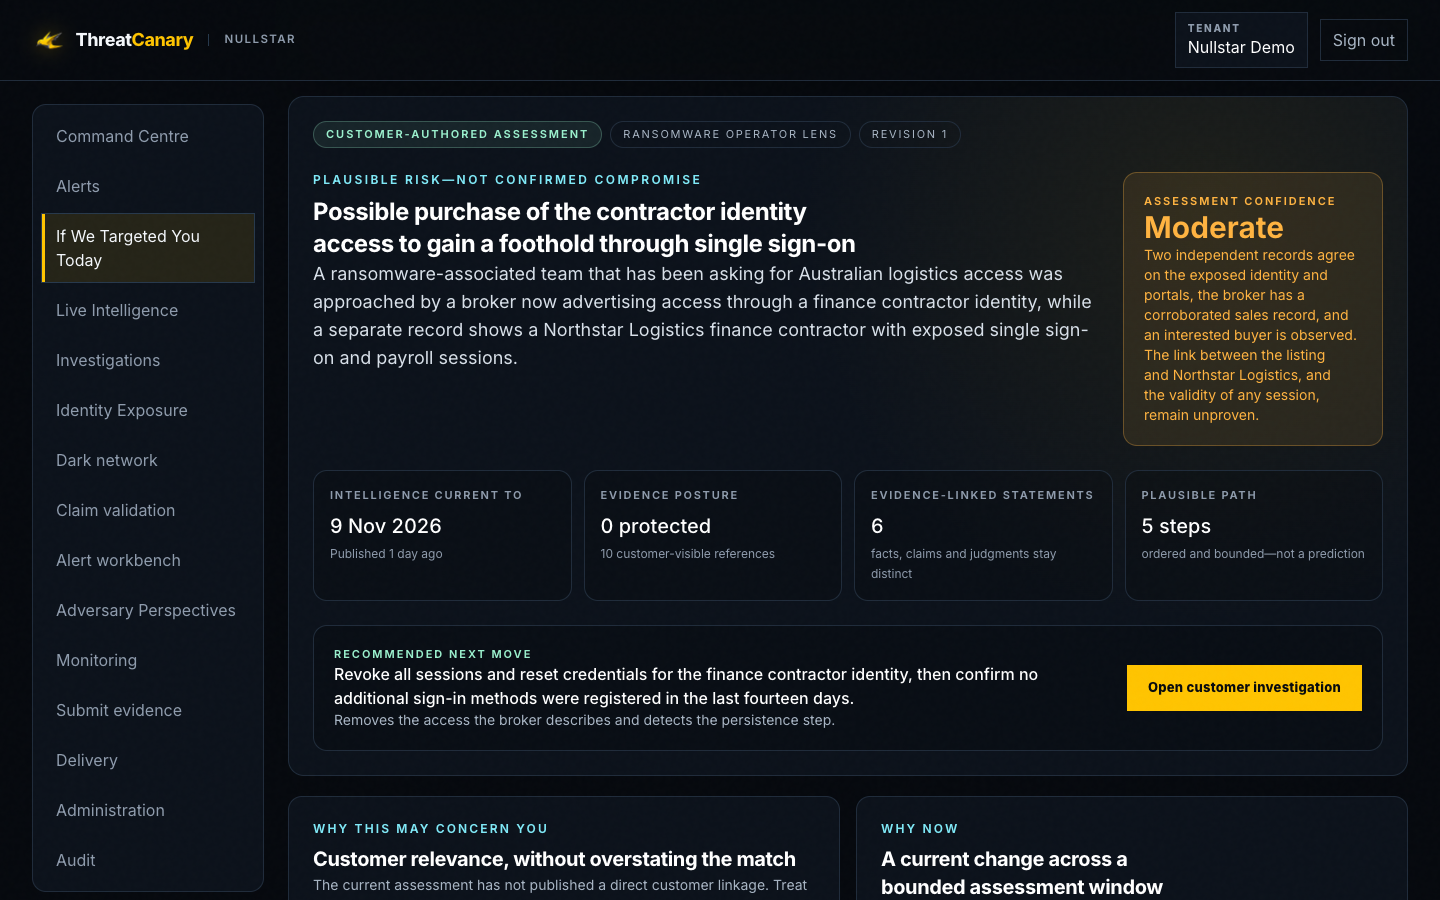
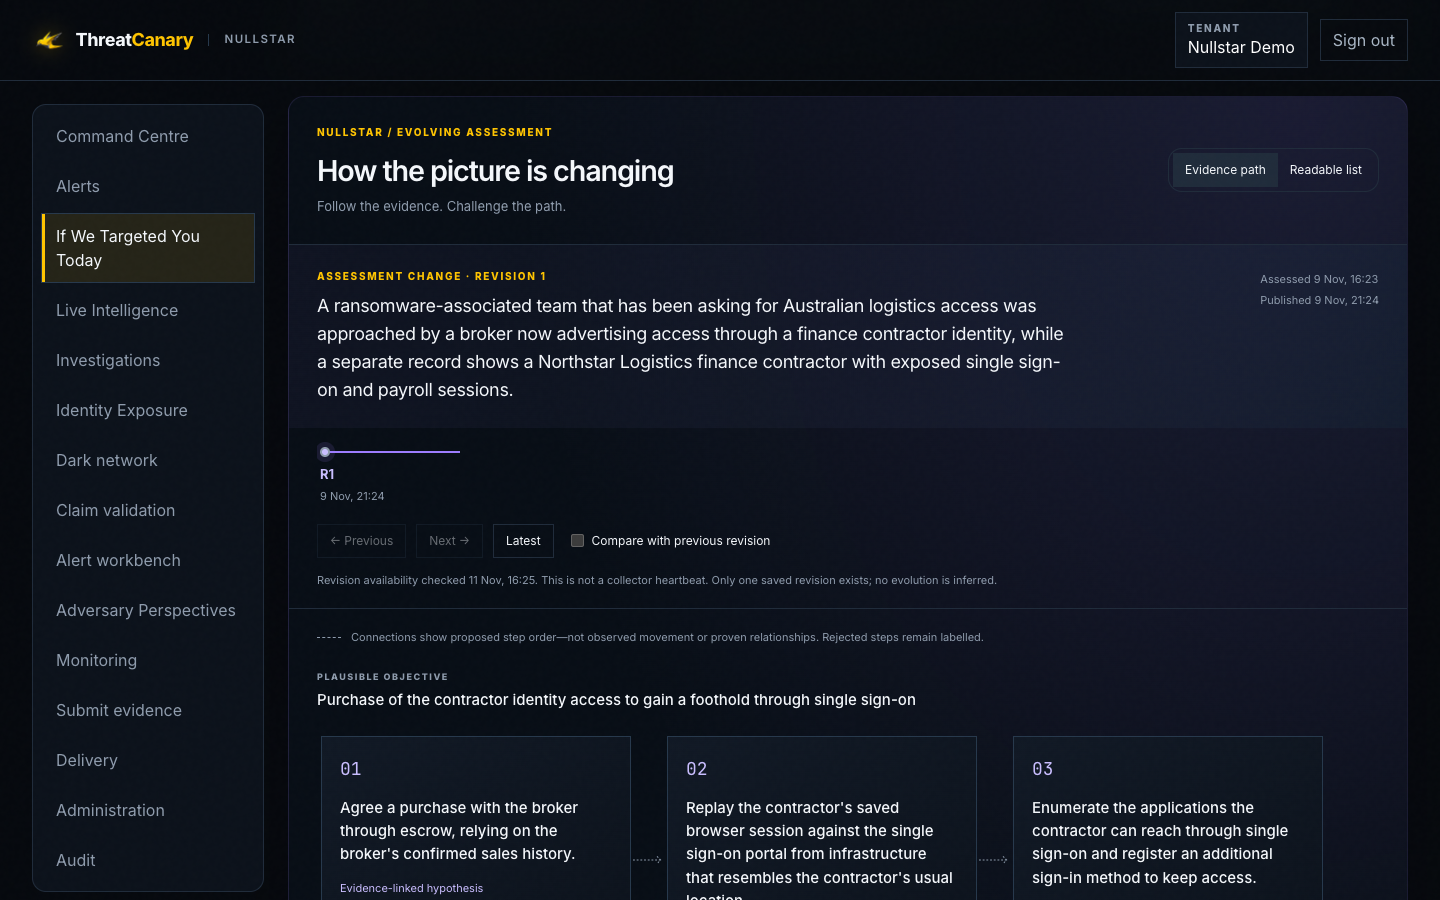
Each perspective is assembled from preserved evidence, challenged by a second analyst and delivered with its confidence rationale, alternatives and revision history.
01Why it matters
- A listing, an exposed identity and a live session rarely arrive together. The danger is the path they form when connected.
- Security teams need to know which defensive move to make first — not a ranked list of unrelated indicators.
- A hypothesis is only useful if it carries its uncertainty and can be revisited as new evidence lands.
02ThreatCanary approach
- Analysts assemble the plausible path from preserved evidence — underground listings, identity exposure and malware signal — with provenance attached to every hop.
- A peer challenges and approves the assessment before it is published; nothing reaches a customer unreviewed.
- Every revision is kept, so your team can walk the history and see how the picture changed.
03What you see
- The plausible path, its confidence rationale, the intelligence chain behind it and the recommended next move.
- What remains uncertain and which alternative explanations were considered.
- Defensive validation steps your team can run against the path today.
04Evidence produced
- Reviewed adversary hypothesis with cited evidence and provenance.
- Full revision history with challenge and approval steps.
- Recommended defensive validation, traceable to the evidence that motivated it.