Underground observatory

Dark-network intelligence

Underground monitoring coverage, community activity and the account histories behind the intelligence — collected by governed connectors that never engage with actors.

Evidence-backedAnalyst-reviewedNo actor engagement

The screen

What your team sees.

Built on the same preserved evidence as every alert and perspective. Open the live demo

Dark-network intelligenceExample tenant
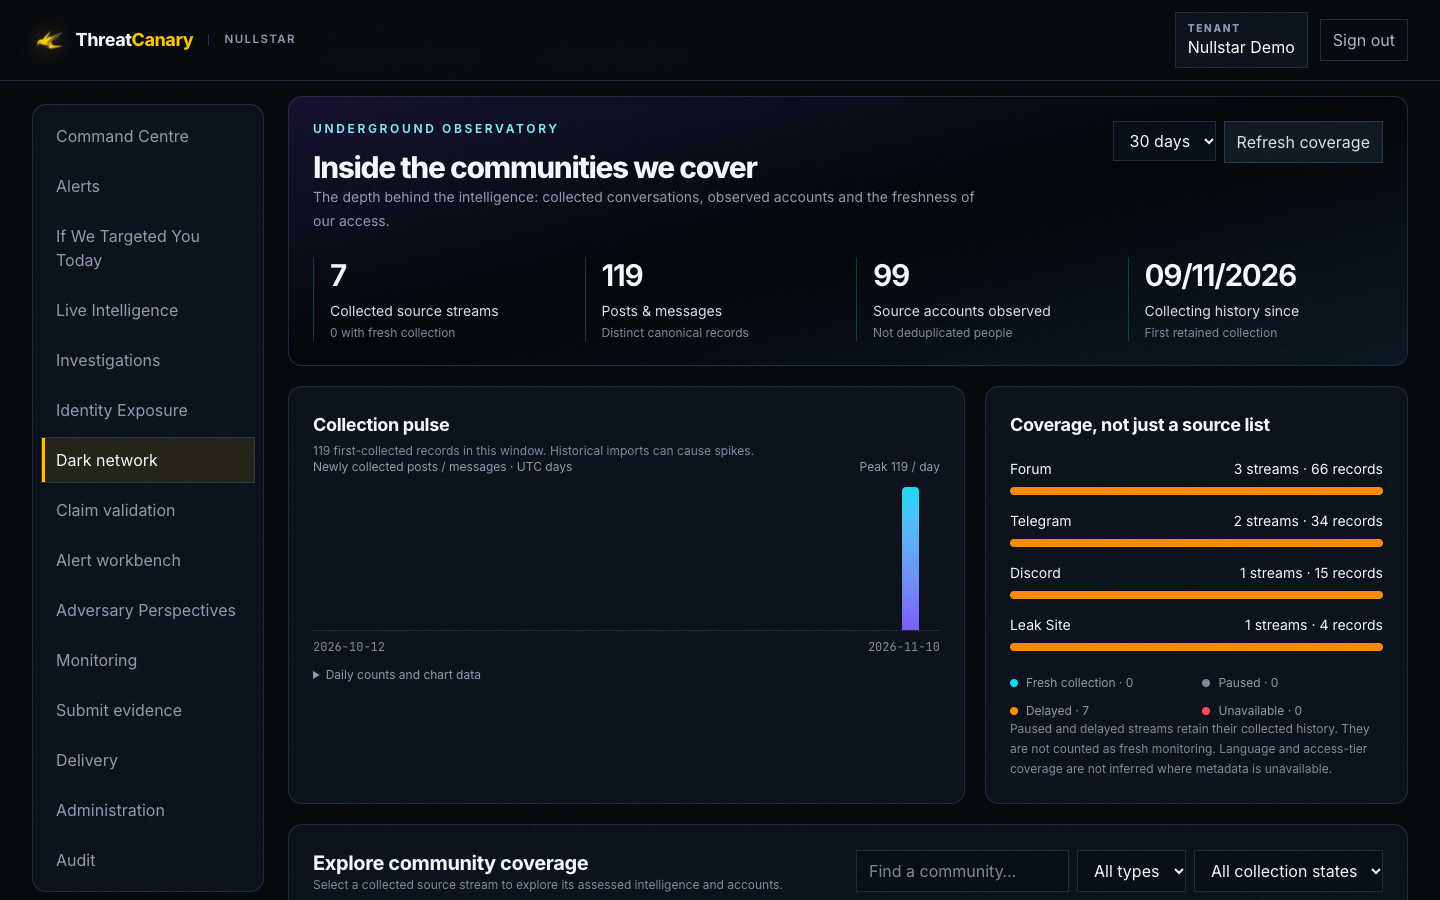
Screenshot: Dark-network coverage — source streams, posts, observed accounts, the collection pulse and coverage by community type.
Capability architecture

Know the source before you trust the claim.

Coverage by community, seller credibility and account histories give every listing the context an analyst needs to decide what the evidence can actually support.

01

Why it matters

  • A listing is a claim by a seller with a reputation to protect or to fake. Its credibility depends on who posted it and how they have behaved.
  • Coverage gaps are invisible unless coverage is measured — a quiet week can mean nothing happened or nothing was collected.
  • Engaging with actors to verify a claim creates legal, ethical and operational risk.
02

ThreatCanary approach

  • Governed connectors collect from forums, markets, leak sites, Telegram and Discord communities, preserving each post with source metadata and capture time.
  • Observed accounts are tracked over time so a claim can be read against its author’s history.
  • No reply farming, messaging, negotiation, purchases or transactions. Where a source hides content behind a fixed action, that action is scripted, limited, logged and approved in advance.
03

What you see

  • Source streams, posts and observed accounts, with the collection pulse and coverage by community type.
  • Seller credibility and account histories that show how a claim’s author has behaved over time.
  • The underground activity feeding your Live Intelligence and alerts.
04

Evidence produced

  • Preserved posts and listings with source metadata and capture time.
  • Account histories and credibility context for claims.
  • Coverage records that show what was collected, and when.
Common questions

Questions teams ask before they commit.

Direct answers on scope, evidence, safety controls and how ThreatCanary differs from tools you already run.

01

Does ThreatCanary post, message or buy on underground forums?

No. Collection is observation only. Nullstar never messages, negotiates, purchases, transacts or validates credentials, and models never initiate or trigger contact with actors. Some sources hide content behind a fixed action; where one is taken it is scripted, limited, logged, approved in advance and can be switched off at once.

02

How is seller credibility assessed?

From the preserved record of how an account has behaved over time — its history across communities, consistency and prior claims — rather than from the reputation a marketplace displays. Analysts record the decision and rationale on each claim they validate.

03

Will I see images or files from underground sources?

No. The workspace never renders images from collected content, and collected material is validated before it is processed or shown.

Evaluate the capability

See this capability work against your attack surface.

Book a product walkthrough